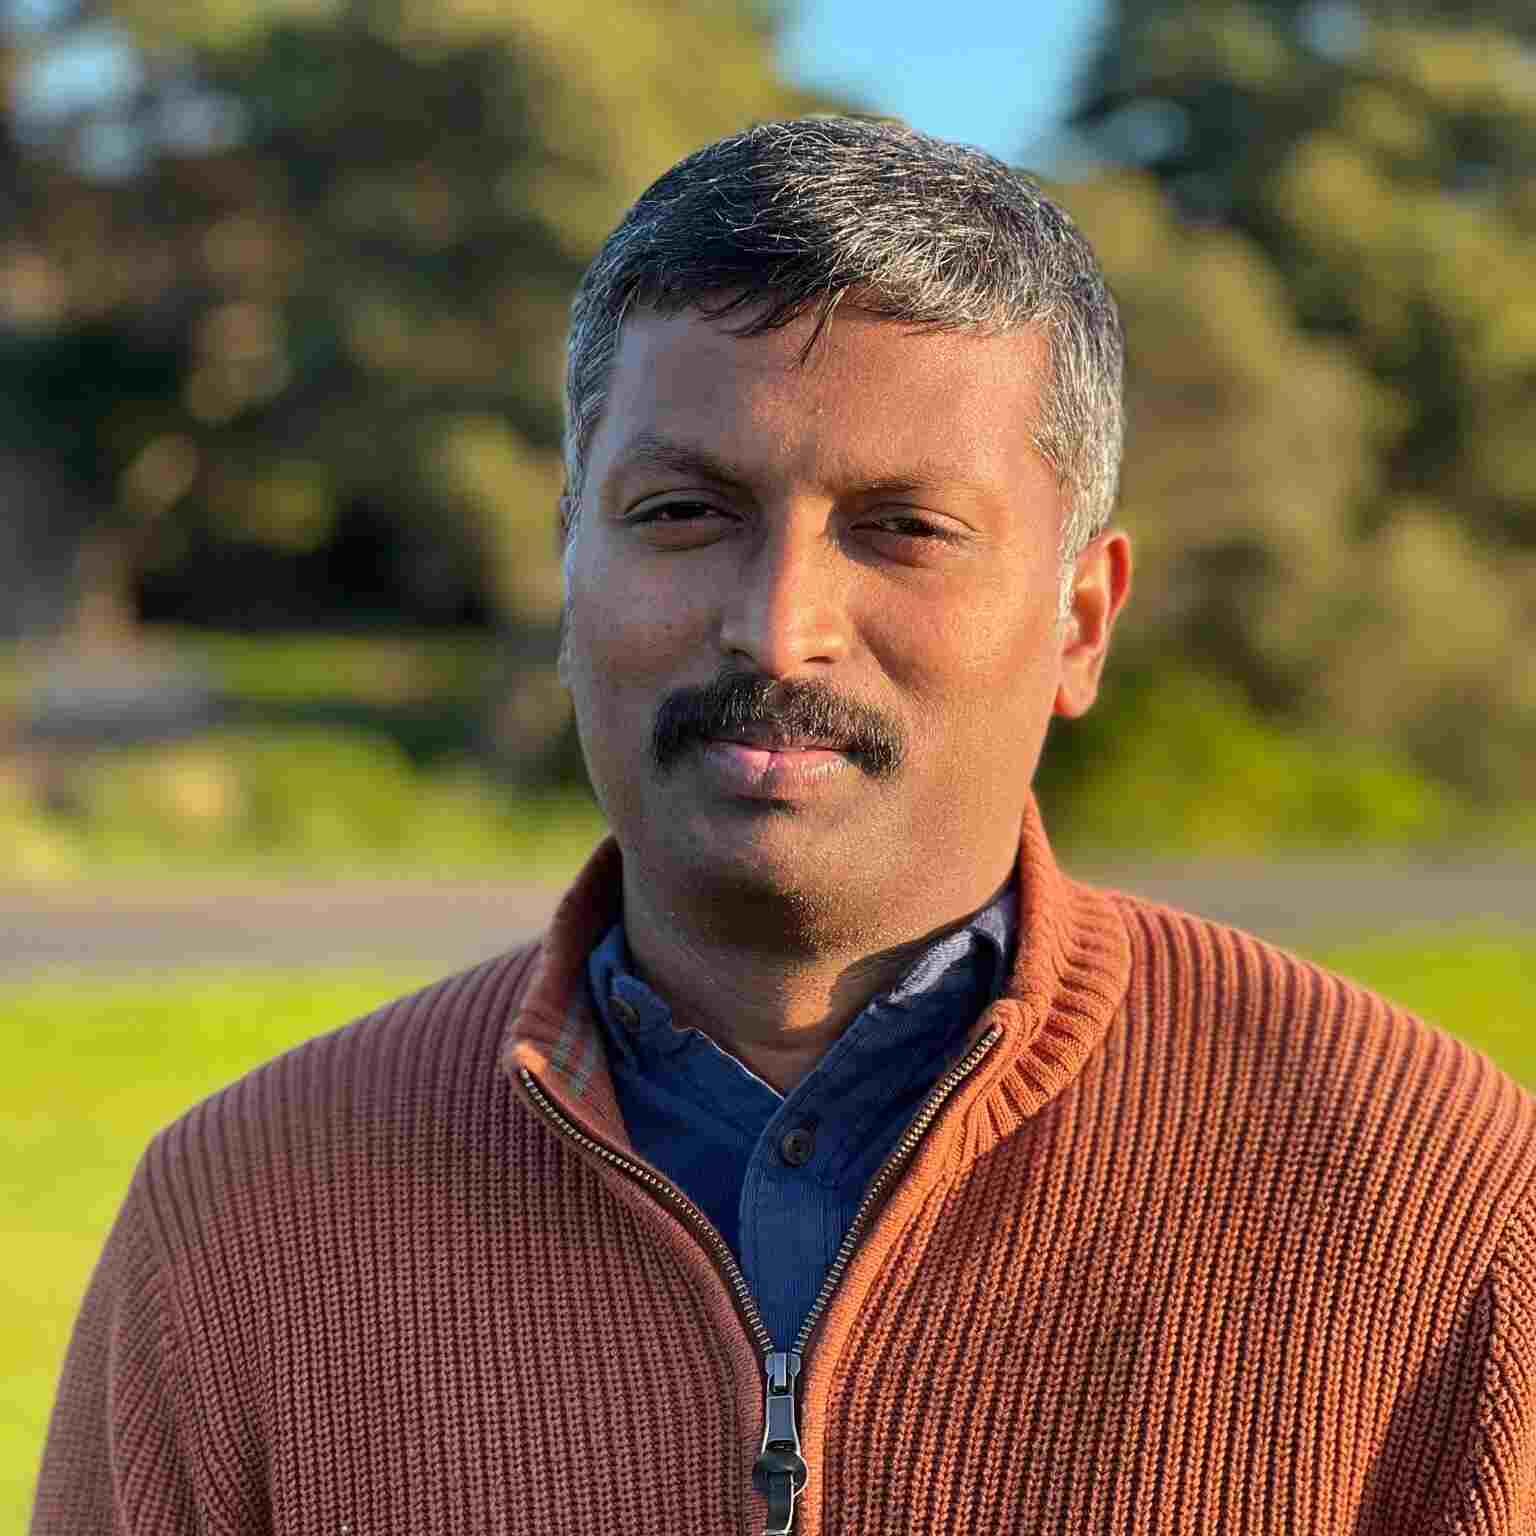
Santhoshkumar Anandakrishnan
Skyline Technology Aus Pty ltd - Melbourne

Eylül 10, 2026 | 6:00 - 7:00 ÖÖ (UTC) Koordineli Evrensel Zaman
Yapay zeka ve en son teknolojileri kullanmaya başlamaya hazır mısınız? Microsoft Reactor geliştiricilerin, girişimcilerin ve startup''ların yapay zeka teknolojisi ve daha fazlasını geliştirmesine yardımcı olmak için etkinlikler, eğitimler ve topluluk kaynakları sağlar. Bize katılın!
Eylül 10, 2026 | 6:00 - 7:00 ÖÖ (UTC) Koordineli Evrensel Zaman
 Canlı Yayın
Konu: Güvenlik
Dil: İngilizce
This session makes the case for "guardrails, not gates": governance that's built into the platform itself rather than bolted on afterward.
We'll start with Azure Policy fundamentals, including policy definitions, initiatives, and effects (Deny, Audit, DeployIfNotExists, Modify), and explore how each effect type is appropriate for different governance scenarios.
From there, we move into practical network security baselines, covering policies that:
The session then zooms out to the Cloud Adoption Framework Landing Zone model, showing how these individual policies are assembled into a coherent governance architecture and applied automatically at subscription vending time. This ensures every new subscription inherits the right guardrails from day one, rather than having security retrofitted later.
We'll also cover:
Konuşmacılar
Santhoshkumar Anandakrishnan
Skyline Technology Aus Pty ltd - Melbourne
Aşağıdaki olaylar da ilginizi çekebilir. Ziyaret etmeye emin olun Reactor giriş sayfası tüm kullanılabilir olayları görmek için.
Biçimlendir:
Canlı Yayın
Konu: Güvenlik
Dil: İngilizce