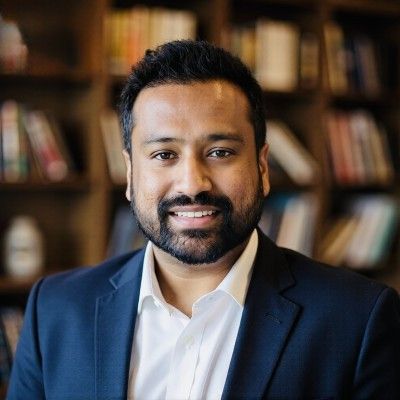
Eshaan Jain
T-Mobile (via Mphasis)

九月 9, 2026 | 5:00 - 6:00 下午 (UTC) 协调世界时
准备好开始使用 AI 和最新技术了吗? Microsoft Reactor 提供活动、培训和社区资源,帮助开发人员、企业家和初创公司利用 AI 技术等。 快加入我们吧!
九月 9, 2026 | 5:00 - 6:00 下午 (UTC) 协调世界时
准备好开始使用 AI 和最新技术了吗? Microsoft Reactor 提供活动、培训和社区资源,帮助开发人员、企业家和初创公司利用 AI 技术等。 快加入我们吧!
九月 9, 2026 | 5:00 - 6:00 下午 (UTC) 协调世界时
 直播
主题: 安全性
语言: 英语
Every CPQ, CLM, and billing rollout I've run wires Salesforce or Vlocity to DocuSign, Stripe or Zuora-type billing, and ERP through API keys and OAuth tokens sitting in DataRaptors, Integration Procedures, and deployment scripts. AppSec teams usually classify that layer as "business configuration," so it never gets scanned the way application code does.
Where credentials actually live in a quote-to-cash stack: middleware scripts, integration procedures, CI/CD for CPQ deployments. Why "business systems" teams don't think of themselves as a scanning target, and what that costs. How GitHub Advanced Security's secret scanning, push protection, and custom patterns close the gap, even for teams that don't see themselves as developers.
A sample repo modeling a CPQ integration script with a hardcoded OAuth token and API key. Push protection blocking a commit in real time. A custom regex pattern built for an enterprise revenue-tool token format. The alert triage view a security lead would actually work from.
主讲人
Eshaan Jain
T-Mobile (via Mphasis)
此活动属于 Spotlight on GitHub Advanced Security Series.
单击此处 访问“系列”页 可在此处查看所有即将举办的活动和点播活动。