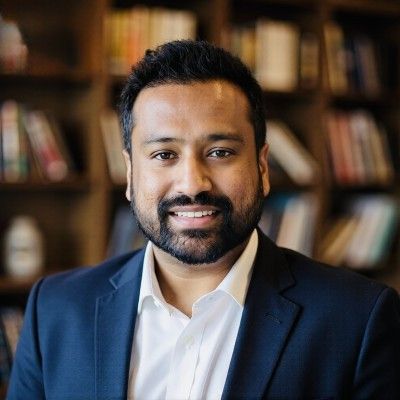
Eshaan Jain
T-Mobile (via Mphasis)

September 9, 2026 | 5.00 - 6.00 PM (UTC) Waktu Universal Terkoordinasi
Siap untuk mulai menggunakan AI dan teknologi terbaru? Microsoft Reactor menyediakan acara, pelatihan, dan sumber daya komunitas untuk membantu pengembang, pengusaha, dan startup dibangun berdasarkan teknologi AI dan banyak lagi. Gabung dengan kami!
September 9, 2026 | 5.00 - 6.00 PM (UTC) Waktu Universal Terkoordinasi
 Streaming Langsung
Topik: Keamanan
Bahasa: Inggris
Every CPQ, CLM, and billing rollout I've run wires Salesforce or Vlocity to DocuSign, Stripe or Zuora-type billing, and ERP through API keys and OAuth tokens sitting in DataRaptors, Integration Procedures, and deployment scripts. AppSec teams usually classify that layer as "business configuration," so it never gets scanned the way application code does.
Where credentials actually live in a quote-to-cash stack: middleware scripts, integration procedures, CI/CD for CPQ deployments. Why "business systems" teams don't think of themselves as a scanning target, and what that costs. How GitHub Advanced Security's secret scanning, push protection, and custom patterns close the gap, even for teams that don't see themselves as developers.
A sample repo modeling a CPQ integration script with a hardcoded OAuth token and API key. Push protection blocking a commit in real time. A custom regex pattern built for an enterprise revenue-tool token format. The alert triage view a security lead would actually work from.
Pembicara
Eshaan Jain
T-Mobile (via Mphasis)
Peristiwa di bawah ini mungkin menarik bagi Anda juga. Pastikan untuk mengunjungi kami Beranda reaktor untuk melihat semua peristiwa yang tersedia.
Format:
Streaming Langsung
Topik: Keamanan
Bahasa: Inggris
Acara ini adalah bagian dari Spotlight on GitHub Advanced Security Series.
Klik di sini untuk kunjungi Halaman Seri di mana Anda dapat melihat semua peristiwa yang akan datang dan sesuai permintaan.